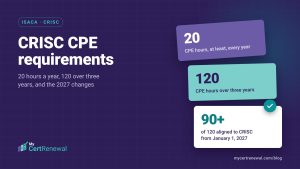
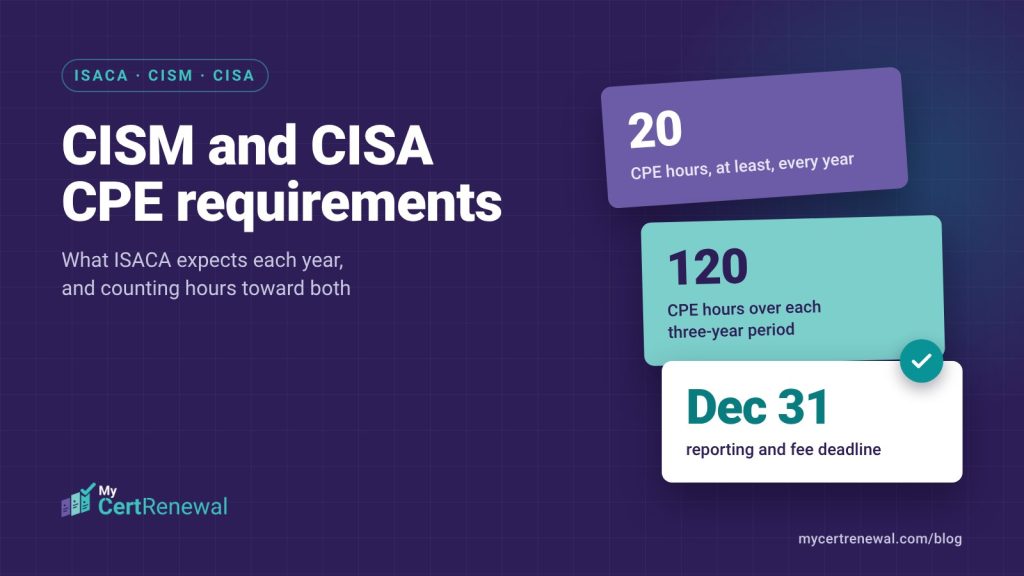
The CISM CPE requirements are the same as CISA’s: report at least 20 CPE hours every year, at least 120 over each three-year reporting period, and pay an annual maintenance fee for each certification. ISACA’s CPE Policy (PDF) puts the payment and reporting deadline at December 31. The same hours can count toward both certifications when the activity maps to each one’s exam content outline.
Most people remember the 120. The 20 is checked every calendar year, so a thin year is a miss even if your three-year total ends up above 120. Rules below were checked on ISACA’s pages on November 1, 2026.
The yearly requirement for CISM and CISA
ISACA’s Maintain CISM and Maintain CISA pages list the same core rules for both:
- Earn and report at least 20 CPE hours a year.
- Earn and report at least 120 CPE hours over the three-year reporting period.
- Pay the annual maintenance fee: US$45 for members, US$85 for non-members.
- Comply with the annual CPE audit if selected, and with ISACA’s Code of Professional Ethics.
CISA adds one more: abide by ISACA’s IT Auditing Standards. ISACA says failing any of these results in revocation.
The ISACA year, month by month
- January 1: the annual reporting period starts. Your three-year period varies and is shown on your annual invoice and compliance letter.
- Through the year: record hours as you earn them in MyISACA under Certification & CPE Management. CPE earned through ISACA is pre-loaded but must be applied: open Report and Manage CPE, find Unapplied CPE Hours and select Apply. Chapter events and other sponsors you report yourself. Keep proof of chapter attendance, since not every chapter posts its CPE to ISACA.
- September onward: ISACA emails and posts maintenance fee invoices for the following year.
- December 31: fee payment and CPE reporting are due, per the CPE Policy. The maintain pages word the fee deadline as 1 January.
The pre-loaded step is easy to miss. ISACA’s maintain pages say pre-loaded hours don’t count toward your requirement until you apply them, and you enter how many go to each certification you hold.
Newly certified? You don’t have to report hours in the year you certified. Your first annual and three-year periods start on January 1 of the next year, and hours earned after your certification date can be reported in that first period.
Holding CISM and CISA together
ISACA lets the same hours count toward more than one ISACA certification when the activity maps to each one’s exam content outline (ECO). The domains are listed on the CISM and CISA certification pages:
| CISM domains | CISA domains |
|---|---|
| Information Security Governance | Information Systems Auditing Process |
| Information Security Risk Management | Governance and Management of Information Technology |
| Information Security Program | Information Systems Acquisition, Development & Implementation |
| Incident Management | Information Systems Operations and Business Resilience |
| Protection of Information Assets |
A session on IT governance may map to both lists. A session on audit sampling probably maps to CISA only. Note which certification each hour supports when you log it, not in December when you report.
- Fees: you pay a maintenance fee for each certification. A third ISACA certification (and any after it) costs US$25 for members and US$50 for non-members.
- Multi-counting: the policy says ISACA Journal quizzes and other ISACA education can count toward each designation you hold, if they align with each ECO.
- Exception: mentoring hours (10 a year at most) can’t be applied to more than one certification.
What changes from January 1, 2027
ISACA’s CPE 2027 page keeps the 120-hour total. At least 90 of those hours must align with the ECO of the certification being renewed, and up to 30 can come from other professional development such as leadership, soft skills, volunteering or mentoring. Vendor sales and marketing demos stop qualifying, though vendor case-study presentations can still count. ISACA says you won’t need a separate set of CPE for each certification you hold, and no system changes happen in the 2026 cycle.
For a CISM and CISA holder, the practical change is one more column in your log: aligned or professional, for each certification. The CRISC CPE guide covers the 2027 split and activity limits in more detail.
How ISACA counts the hours
One CPE hour is 50 minutes of active participation, excluding lunches and breaks, reported in quarter hours. ISACA’s own example is a 9 a.m. to 5 p.m. day with two 15-minute breaks and an hour for lunch. That leaves 390 minutes, and 390 divided by 50 is 7.8, reported as 7.75 CPE hours. Not 8.
If you are selected for an audit
ISACA audits a random sample each year. If you are picked, you provide supporting documentation for all reported activities from a specific calendar year. Each record should show your name, the sponsoring organization, the activity title and description, the date and the CPE hours. A letter, certificate of completion, attendance roster or Verification of Attendance form all work.
ISACA’s own pages disagree on retention. The maintain pages say 12 months after the end of each three-year cycle; the revised policy PDF says a minimum of three years. Keep records for whichever is longer.
Not complying with an audit means revocation. If an appeal for reinstatement is approved, you pay any outstanding maintenance fees plus a US$50 reinstatement fee for each certification. The policy applies that fee when the revocation has been outstanding for more than 60 days.
A one-page annual checklist
- At least 20 hours reported for CISM, and at least 20 for CISA.
- Pre-loaded ISACA hours applied to each certification.
- Three-year total on pace for 120 (about 40 a year).
- Each hour tagged aligned or professional, for each certification.
- Maintenance fee paid for each certification.
- Proof saved for every activity, with the six details ISACA lists.
Keeping CISM and CISA in one place
MyCertRenewal has ISACA credit rules built for CISA, CISM and CRISC (see supported certifications). You log an activity once and see where it can count toward each certification you hold, and each claim keeps its own status, from identified through accepted. The certificate attaches to the activity, so one file supports every claim (audit-ready evidence). Reminder emails can warn you before a cycle deadline while you are still short (notifications and reminders). You still report in MyISACA yourself.
If CISM and CISA are your two certifications, the Free plan covers both. Start free, no card needed.
Frequently asked questions
How many CPE hours do I need each year for CISM?
At least 20 CPE hours every year and at least 120 over the three-year reporting period, according to ISACA’s Maintain CISM page. CISA has the same requirement.
When are ISACA CPE hours and fees due?
ISACA’s CPE Policy says the maintenance fee and CPE reporting are due by December 31. The Maintain CISM and CISA pages word the fee deadline as 1 January. Invoices go out from September for the following year.
Can the same CPE hours count toward CISM and CISA?
Yes, when the activity maps to the exam content outline of each certification. Mentoring hours are the exception: they can’t be applied to more than one certification.
How much are the ISACA maintenance fees if I hold CISM and CISA?
US$45 a year per certification for ISACA members and US$85 for non-members. If you add a third ISACA certification, it costs US$25 for members and US$50 for non-members.
What does an ISACA CPE audit ask for?
Supporting documentation for all reported activities from a specific calendar year. Each record should show your name, the sponsoring organization, the activity title and description, the date and the CPE hours.
Certification rules change. Always confirm current requirements with the certifying body. MyCertRenewal is not affiliated with ISACA.